• Send Us A Tip
  • Calling all Tech Writers
  • Advertise
Friday, October 9, 2026
  • Login
TechStory
  • News
  • Crypto
  • Gadgets
  • Memes
  • Gaming
  • Cars
  • AI
  • Startups
  • Markets
  • How to
No Result
View All Result
  • News
  • Crypto
  • Gadgets
  • Memes
  • Gaming
  • Cars
  • AI
  • Startups
  • Markets
  • How to
No Result
View All Result
TechStory
No Result
View All Result
Home Business

Apple Health leaders misled executives, punished staff members

by Manasi Varma
October 6, 2021
in Business, Gadgets, Other, Tech
Reading Time: 2 mins read
0
Is the production issue for Apple Watch Series 7 resolved?

Is the production issue for Apple Watch Series 7 resolved? Image Credits: Verge

TwitterWhatsappLinkedin

Apple Insiders say that Apple Health leaders have misled executives, and have even punished staff members. They have alleged that leaders often exaggerate results and crack down on staff who object to their moves.

You might also like

How Businesses Use Mobile Proxy Servers for Localized Data Collection

Navi Eyes $40 Mn Funding as IPO Plans Take Shape

Ola Electric Eyes ₹1,000 Cr Rights Issue at 26% Discount

Misleading Optimism

A new report by Business Insider claims that Apple has Apple’s health projects are being marred due to a lack of direction, as well as a “misleading optimism” from team heads. And that’s not all, as staff who dissent against orders are sidelined, or asked to leave the company altogether.

For example, Health’s Dr. Will Poe resigned in December 2019, when he had written a letter claiming that Apple COO Jeff Williams was being fed fake optimistic data about the challenges.

One former employee has said that a number of workers “risked their careers” to contact the HR regarding the state of things, adding that that company is satisfied with the “current status quo,” and isn’t keen on helping.

Another employee asserts that the fact that staff aren’t comfortable informing execs that things aren’t going as planned, speaks volumes about the quality of the products available on the market or up for production.

Clinical Staff Sidelined for Voicing Opinion

In its report, Insider claims to have reviewed multiple internal documents, and interviewed 11 current and former staff members at Apple. It says that three of these employees assert that Apple Watch’s health features are introduced by the engineering staff, and not by the clinical ones.

In fact, clinical staff have even been deterred from providing specific health ideas or studies. Nevertheless, the report also claims that collaboration between the two units has been rising lately.

A former employee has claimed that the firm didn’t have a “visionary leader” who could drive the group towards a “singular goal.” Apparently, the Apple Watch is designed only to identify health issues, not measure them. But that doesn’t stop the firm from advertising the latter as a use of the product.
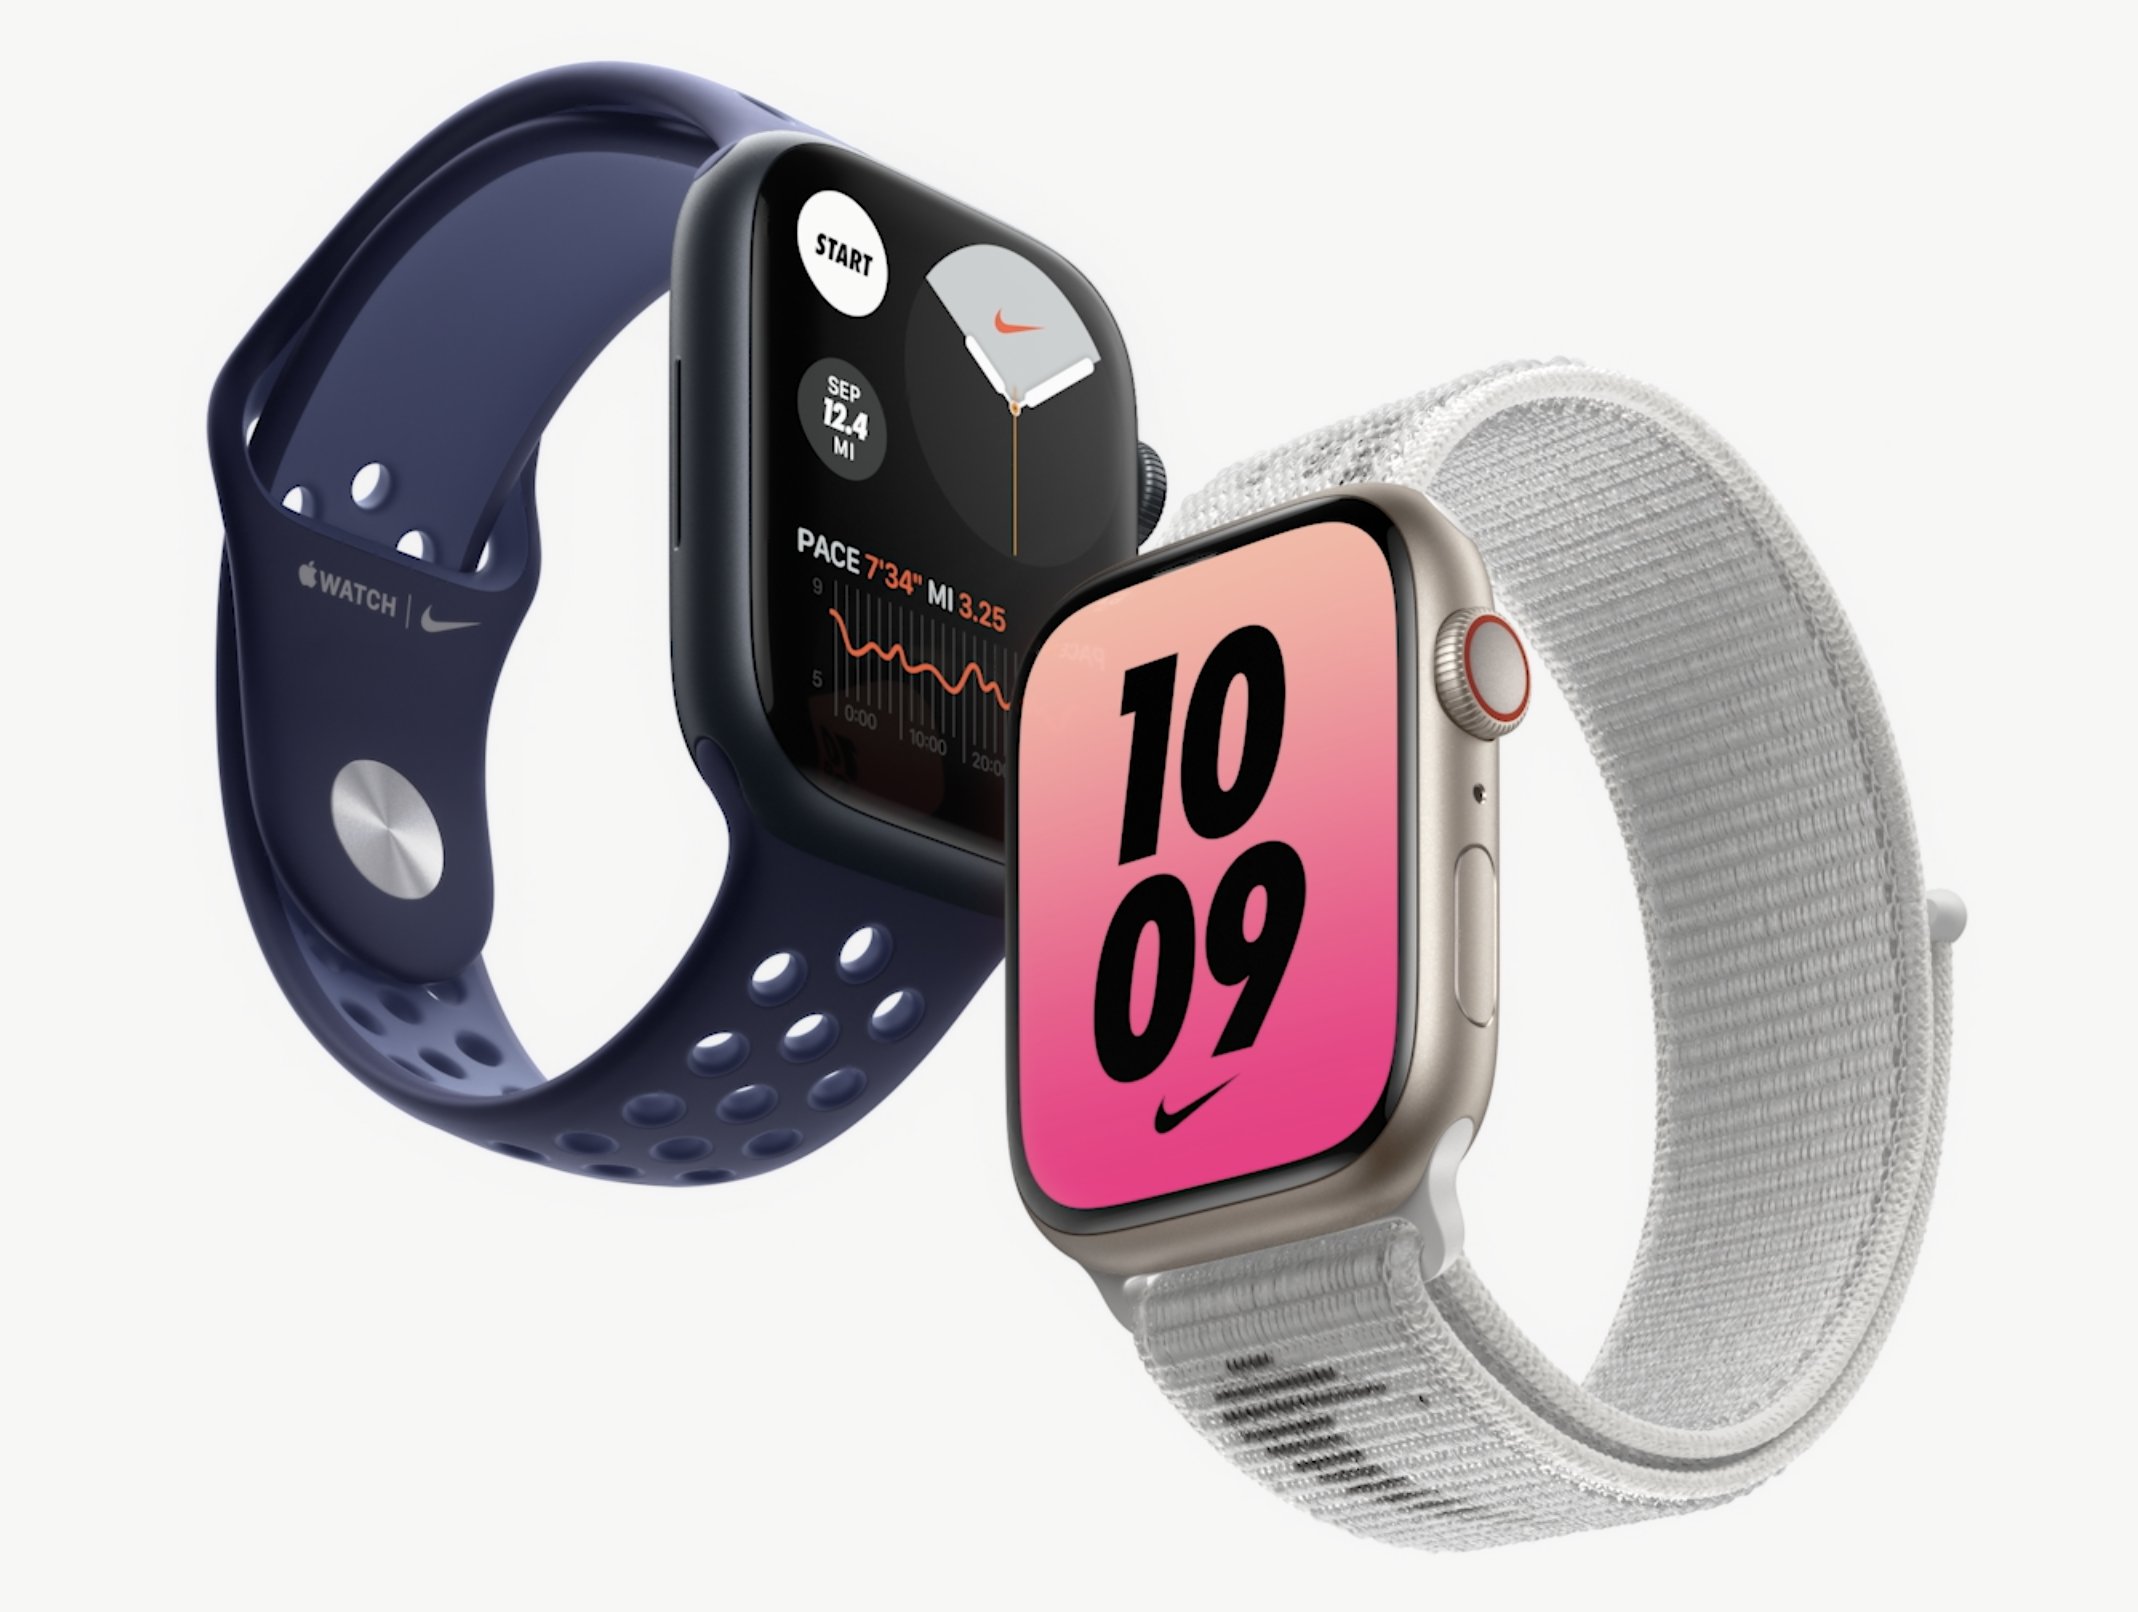
What does IP6X and WR50 ratings mean for Apple Watch Series 7?
Image Credits: Apple

Dr. Sumbul Desai, who had been appointed as the head of Apple Health’s clinic trials in 2019, has previously been criticized for sidelined staff members who spoke out regarding the poor health facilities at the clinics.

Do What’s Right

In response, company spokesperson Fred Sainz has disputed the allegations, claiming that the criticisms rely on inaccurate or incomplete information. He adds that contrary to the accusations, health leaders actually urge employees to “do what’s right,” by speaking up.
 

Tags: AppleApple watchJeff WilliamsSumbul Desai
Tweet54SendShare15
Previous Post

MekaVerse: 100k Discord Members In 48 Hours

Next Post

Online learning Platform Udemy files for an IPO at NASDAQ

Manasi Varma

A 20-something year old with a flair for writing, a love for reading, and an obsession for KPop. Most amicable person you'll ever meet.

Recommended For You

How Businesses Use Mobile Proxy Servers for Localized Data Collection

by Rohan Mathawan
October 9, 2026
0
Engineering teams building market intelligence pipelines frequently deal with rate limits and manipulated pricing data. Target platforms actively manage incoming traffic using security tools like Web Application Firewalls and TLS fingerprinting. Relying on commercial server nodes for data extraction often leads to interrupted sessions. To solve this, businesses are moving their infrastructure toward authentic cellular networks. Using mobile proxy servers allows them to collect accurate, localized web data reliably. TL;DR: Core benefits of mobile proxy servers for data extraction Carrier-grade trust: Mobile networks use CGNAT, masking your automated traffic alongside thousands of real smartphone users, resulting in maximum IP trust scores. Organic IP shifts: Security systems are adapted to mobile networks where IP addresses routinely change across local cell towers. A dynamic IP is completely natural, provided your geographic region and device footprint remain consistent. Dedicated vs. shared hardware: Dedicated modems allow manual IP rotation via API but require a 5 to 10-second pause while the physical hardware reboots. Shared proxies offer fixed-interval rotation without interrupting active users. Maintaining stable access: Premium infrastructures use the VLESS protocol to route proxy connections as standard HTTPS browsing. This helps maintain connections in environments with strict local ISP filtering. Why localized data extraction requires authentic connections Companies extract localized web data to see information exactly as it appears to a regular user in a specific region. Pricing and availability change based on the viewer's location. A consumer searching a travel aggregator from London sees different flight options than a user querying the exact same route from Tokyo. Teams historically built scraping infrastructure on data center IPs. Today, anti-fraud engines maintain strict databases of commercial cloud subnets. When a firewall detects consumer-level requests coming from a corporate server, it ruins the connection's trust score. Real users do not browse from cloud data centers. The target platform simply responds with CAPTCHAs or HTTP 429 errors. How mobile proxy servers maintain stable access To ensure stable data collection, automated traffic needs to match the normal network patterns of genuine human users. Mobile proxy servers accomplish this by routing requests through real 4G LTE or 5G modems equipped with authentic SIM cards. This works through Carrier-Grade NAT (CGNAT). Mobile carriers do not assign a unique public IP to every smartphone. Instead, they push the data streams of thousands of subscribers onto the internet through a single shared IP address. Banning a CGNAT mobile IP means disconnecting hundreds of real retail consumers in that area. To avoid this collateral damage, security engines treat mobile carrier ASNs with extreme leniency, granting them trust scores between 90% and 99%. Infrastructure Type Network Source CGNAT Shielding Average Trust Score Algorithmic WAF Reaction Data Center Commercial Cloud Providers No (1:1 routing) 20% - 40% Immediate block, CAPTCHA, or rate-limit for consumer endpoints. Static Residential Home Internet Providers Rare (Usually 1:1) 70% - 85% Reliable for steady sessions, but flagged during abrupt traffic spikes. Mobile (LTE/5G) Real Cellular Carrier Networks Yes (Thousands to 1) 90% - 99% High tolerance; blocking is mathematically prohibitive due to collateral damage. IP rotation: Why dynamic addresses are natural for mobile proxy servers Many operators believe that keeping a static, unchanging IP address is the only way to maintain a healthy session. They assume an IP rotation during a collection task immediately triggers security algorithms. In reality, the internet is heavily adapted to a mobile-first world. When genuine consumers browse on their smartphones, they commute across a city and experience brief signal drops. These physical events force their hardware to re-authenticate with the network. The mobile carrier then assigns the device a brand-new IP address from the regional pool. Target platforms inherently expect this behavior. Consequently, an IP address changing within the bounds of a specific city or county is not an automatic red flag. What actually triggers anti-fraud systems is inconsistency in the digital footprint. As long as the regional origin and the device identity remain synchronized, the session remains valid. Modern automation relies entirely on consistent device and location profiles rather than rigid IP addresses. Choosing the right mobile proxies: Dedicated vs. Shared hardware When integrating cellular infrastructure into a pipeline, engineering teams must decide between two distinct types of mobile proxies. This choice directly impacts hardware control and session persistence. Dedicated proxies Dedicated mobile proxies provide an operator with exclusive, single-tenant access to a specific physical modem and SIM card. This grants unrestricted bandwidth and absolute programmatic control over the connection. Operators can trigger an IP change precisely when their workflow demands it via an API call integrated directly into their Python or Node.js scripts. Developers need to handle the rotation delay. When the API command executes, the physical modem drops its connection to the local cell tower and renegotiates a new one. This reset takes 5 to 10 seconds. Scripts require deliberate pauses (e.g., time.sleep(10)) during this window. Sending payloads before the modem re-authenticates causes timeout errors. Shared proxies Shared mobile proxies allow multiple independent users to route their traffic through the same physical 5G/LTE modem simultaneously. Because the connection is multiplexed, the IP address on a shared port rotates at a strict, automated interval typically every 5 or 30 minutes. Manual rotation is disabled because resetting the network would drop the connection for everyone sharing the hardware. Shared ports provide cost-effective CGNAT trust for stateless tasks. Shared networks provide excellent, cost-effective CGNAT trust for stateless tasks where session persistence is irrelevant. Handling deep packet inspection with VLESS While mobile proxy servers manage external routing, businesses sometimes face interference from their own local Internet Service Provider (ISP). Some local ISPs use Deep Packet Inspection (DPI) to monitor outbound traffic. Standard proxy protocols have recognizable cryptographic handshakes that DPI systems often restrict. To resolve this, premium mobile infrastructure supports the VLESS protocol. Rather than generating a custom proxy certificate, VLESS borrows the cryptographic signature of a highly trusted, unrelated domain during the TLS handshake. Local DPI tools analyze this outbound data flow and see standard HTTPS web browsing. This allows data teams to work without local network interruptions. Digital identity and environment setup High-trust IP addresses lose their value if a script logs into an account using a flagged VoIP phone number. The same happens if a localized payment uses a card that mismatches the proxy's geographic location. Operators pair dedicated mobile IP connections with clean browser profiles. They use tokenized payment cards matching the proxy's billing region and real residential phone numbers for SMS verifications. Sourcing these components from different providers slows down infrastructure deployment. Platforms like CyberYozh App consolidate these tools. Teams deploy dedicated mobile IPs, issue virtual cards, and rent local ISP numbers from a single ecosystem. Checking the complete setup through a built-in fraud scorer ensures a highly trusted profile before data extraction begins. Real-world application A market intelligence firm monitored retail pricing across European e-commerce platforms using data center proxies. Within days, the target platform recognized the commercial subnets, applied rate limits, and served manipulated HTML. The firm restructured its pipeline. They replaced their data center nodes with CyberYozh dedicated mobile proxies physically located in the target countries. Because the requests originated from genuine 4G/5G mobile gateways shielded by CGNAT, the firewall perceived the traffic as authentic mobile shoppers. The Python script held a single mobile IP for a persistent session, extracting the localized pricing data. Once a geographic sweep was complete, the script fired an API rotation call, paused operations for 10 seconds while the physical modem reset its radio link to the local cell tower, and seamlessly resumed collection on the next batch of URLs. By aligning their geographic footprint and accounting for the physical realities of hardware rotation, the firm restored stable access to their target data. Final thoughts on mobile proxy infrastructure Basic data collection methods struggle against modern traffic analysis. Because international platforms look closely at connection behavior to protect their localized data, relying on commercial server networks often leads to unstable access. Authentic LTE and 5G cellular hardware solves this problem. Carrier-Grade NAT and API rotation align the traffic with natural network behavior. This approach secures high IP quality and enables reliable data extraction at scale. As businesses rely more on location-specific data, the technology behind reliable web access is becoming an important part of modern data collection. For more practical guides on emerging technology, online infrastructure, and digital tools, explore Kemotech.

Engineering teams building market intelligence pipelines frequently deal with rate limits and manipulated pricing data. Target platforms actively manage incoming traffic using security tools like Web Application Firewalls...

Read more

Navi Eyes $40 Mn Funding as IPO Plans Take Shape

by Ishaan Negi
October 8, 2026
0
Sachin Bansal Steps Down as CEO, Takes on Executive Chairman Role at Navi

Navi, the financial services company led by Flipkart co-founder Sachin Bansal, is looking to raise around $40 million from Elevation Holdings as it strengthens its finances ahead of...

Read more

Ola Electric Eyes ₹1,000 Cr Rights Issue at 26% Discount

by Ishaan Negi
October 8, 2026
0
Ola Electric Eyes ₹1,000 Cr Rights Issue at 26% Discount

Ola Electric is looking to raise ₹1,000 crore through a rights issue, offering new shares at ₹27 apiece as the electric vehicle maker seeks fresh funds to strengthen...

Read more
Next Post
Online education platform, Udemy acquired funds worth $100M reaching $3.3B valuation

Online learning Platform Udemy files for an IPO at NASDAQ

Please login to join discussion

Techstory

Tech and Business News from around the world. Follow along for latest in the world of Tech, AI, Crypto, EVs, Business Personalities and more.
reach us at info@techstory.in

Advertise With Us

Reach out at - info@techstory.in

Aviator Game India 2026

BROWSE BY TAG

#Crypto #howto 2024 acquisition AI amazon Apple Artificial Intelligence bitcoin Business China cryptocurrency e-commerce electric vehicles Elon Musk Ethereum facebook funding Gaming Google India Instagram Investment iPhone IPO Market Markets Meta Microsoft News OpenAI samsung Social Media SpaceX startup startups tech Tech news technology Tesla TikTok trend trending twitter US

© 2025 Techstory.in

No Result
View All Result
  • News
  • Crypto
  • Gadgets
  • Memes
  • Gaming
  • Cars
  • AI
  • Startups
  • Markets
  • How to

© 2025 Techstory.in

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In
Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?