• Send Us A Tip
  • Calling all Tech Writers
  • Advertise
Friday, September 25, 2026
  • Login
TechStory
  • News
  • Crypto
  • Gadgets
  • Memes
  • Gaming
  • Cars
  • AI
  • Startups
  • Markets
  • How to
No Result
View All Result
  • News
  • Crypto
  • Gadgets
  • Memes
  • Gaming
  • Cars
  • AI
  • Startups
  • Markets
  • How to
No Result
View All Result
TechStory
No Result
View All Result
Home News

After Wanna Cry Havoc, Judy Malware Infects 36.5 million Android Phones!

by
May 30, 2017
in News
Reading Time: 2 mins read
0
judy malware attack
TwitterWhatsappLinkedin

judy malware attack

You might also like

Australia Investigates OpenAI AI Agent After Unauthorised Medicare Portal Access

Praxis Plans $1 Bn AI and Crypto-Powered Community in Uruguay

Sarvam AI Launches Saaras V4 With Multilingual Speech Recognition Capabilities

30 May 2017, India:

ANDROID USERS, THIS ONE IS FOR YOU! After the havoc caused by the Wanna Cry ransomware, a new virus called ‘Judy’ has infected around 36.5 million Android users globally!

“Some of the apps (that were infected) we discovered resided on Google Play for several years, but all were recently updated. It is unclear how long the malicious code existed inside the apps, hence the actual spread of the malware remains unknown, security solutions firm Check Point said in a blog post.

Google has removed 41 Android apps which were infected with Judy from the official Play Store. It appears that starting with April 2016, the apps were slowly updated with malicious code. The purpose of this code was to launch a browser app, load an URL, and use JavaScript to locate and click on specific banners that would bring profits to the malware’s creators.

To elaborate, When a user downloads and installs a malicious app, the malware infects the device but stays inactive. After the program itself is accessed, the malware uses the user’s connection to establish a link with the Command and Control server, which is the developer’s own server. This app then redirects and keeps opening external web pages. Once the targeted website is launched, the Judy virus uses the JavaScript code to locate and click on banners from the Google ads infrastructure.

Related read- Top 10 Hacks of 2016: The Largest, The Deadliest And The Craziest!

According to Check Point, almost all malicious apps were made by a South Korean company called Kiniwini, but registered on the Google Play Store as ENISTUDIO corp. It is unclear if the company added the malicious code itself, or its servers were compromised and the code added by a third-party.

The Judy virus has been compared to two other similar exploits, namely FalseGuide and Skinner. The developers of these programs usually find ways of increasing the positive ratings of their apps to lure new users. In some cases, actual users are unknowingly forced to give high ratings to the app as per the report by Blasting News. Check Point advises users against relying only on the Play Store securities. It is instead better to use some form of external protection such as anti-virus and anti-malware software, to protect one’s devices against such malicious apps. (Image- wallpaperup.com)

Also read- ATM Will be Shutdown Due to Ransomware Attack; If You’re Forwarding Such Messages, You Need to Read This!

Tags: Android phonesGoogle playGoogle Play hackedHackJudyMalwareViruswanna cry
Tweet54SendShare15
Previous Post

Adobe To Make Virtual Reality Headset With An Improved Feature

Next Post

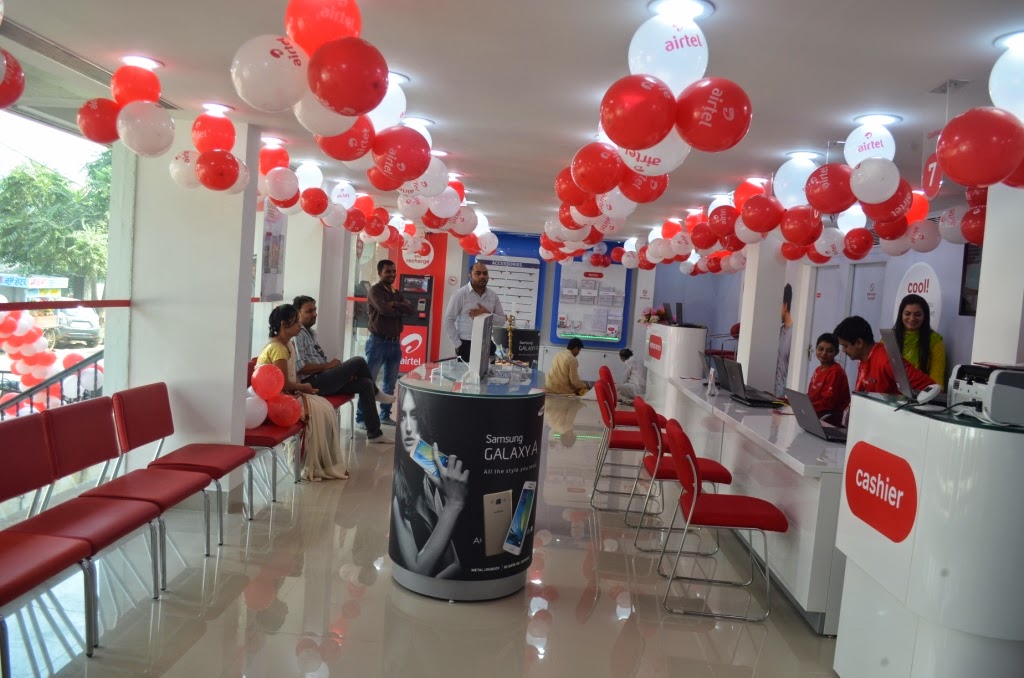
Airtel Payments Bank’s Customer Base Acquired Ethically?

Recommended For You

Australia Investigates OpenAI AI Agent After Unauthorised Medicare Portal Access

by Ishaan Negi
September 24, 2026
0
Australia Investigates OpenAI AI Agent After Unauthorised Medicare Portal Access

An OpenAI artificial intelligence agent gained unauthorised access to an Australian Government Medicare statistics portal in June, accessing both public and non-public files and prompting an urgent investigation...

Read more

Praxis Plans $1 Bn AI and Crypto-Powered Community in Uruguay

by Ishaan Negi
September 24, 2026
0
Praxis Plans $1 Bn AI and Crypto-Powered Community in Uruguay

Praxis, a technology-focused company building around artificial intelligence, cryptocurrency and internet-native communities, has announced plans to develop a new tech-oriented enclave in Uruguay. The first phase of the...

Read more

Sarvam AI Launches Saaras V4 With Multilingual Speech Recognition Capabilities

by Ishaan Negi
September 23, 2026
0
Sarvam Joins the Unicorn Club: Why India’s Biggest AI Bet Comes at the Perfect Time

Indian artificial intelligence startup Sarvam AI has launched Saaras V4, the latest version of its automatic speech recognition (ASR) model, with a focus on multilingual speech, Indian languages...

Read more
Next Post
Airtel Payments Bank’s Customer Base Acquired Ethically?

Airtel Payments Bank's Customer Base Acquired Ethically?

Please login to join discussion

Techstory

Tech and Business News from around the world. Follow along for latest in the world of Tech, AI, Crypto, EVs, Business Personalities and more.
reach us at info@techstory.in

Advertise With Us

Reach out at - info@techstory.in

Aviator Game India 2026

BROWSE BY TAG

#Crypto #howto 2024 acquisition AI amazon Apple Artificial Intelligence bitcoin Business China cryptocurrency e-commerce electric vehicles Elon Musk Ethereum facebook funding Gaming Google India Instagram Investment iPhone IPO Market Markets Meta Microsoft News OpenAI samsung Social Media SpaceX startup startups tech Tech news technology Tesla TikTok trend trending twitter US

© 2025 Techstory.in

No Result
View All Result
  • News
  • Crypto
  • Gadgets
  • Memes
  • Gaming
  • Cars
  • AI
  • Startups
  • Markets
  • How to

© 2025 Techstory.in

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In
Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?